AIO has completed a SOC 2 Type II examination by A-LIGN, covering the security and confidentiality of restaurant data on our platform.
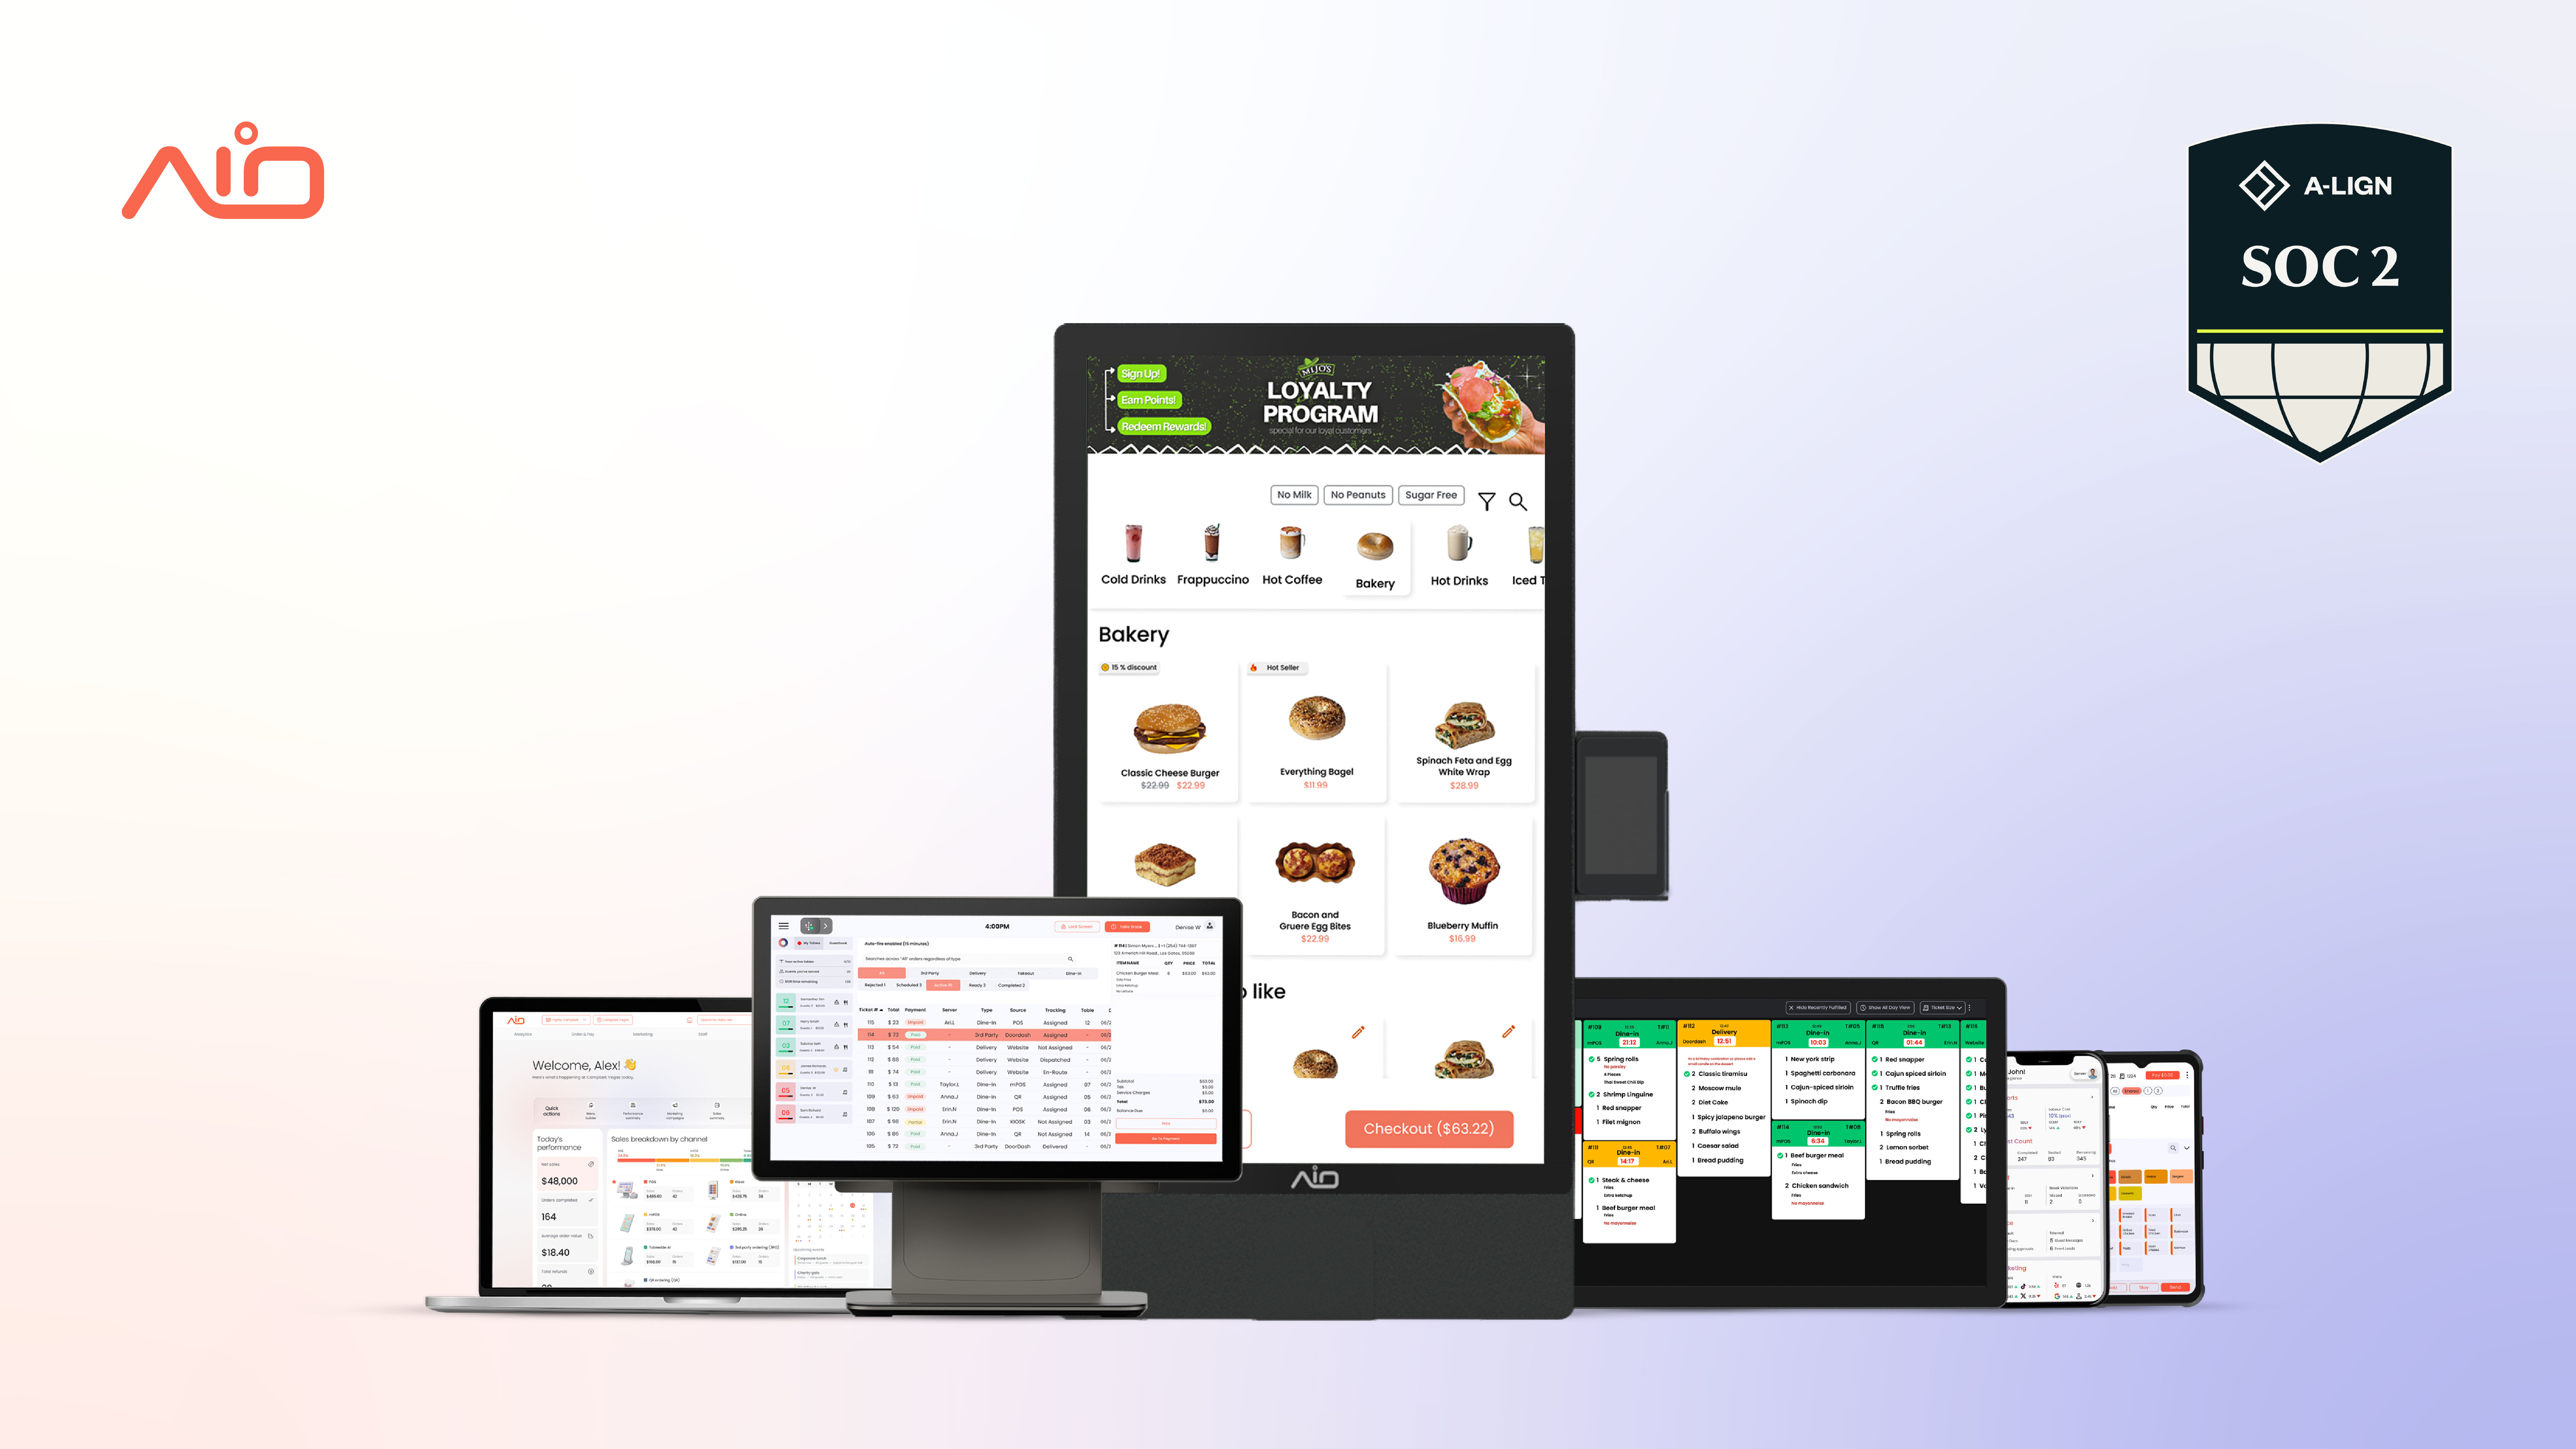
November 13, 2026. We're proud to announce that AIO has achieved SOC 2 Type II compliance. It is one of the most significant milestones in our company's history and a clear reflection of our commitment to protecting restaurant data. Every restaurant on AIO now runs on a platform whose security has been independently examined.
The audit was conducted by A-LIGN, one of the most established names in cybersecurity compliance. A-LIGN has completed more than 13,800 SOC 2 audits and works with more than 6,400 organizations, including SAS, TeamViewer, Boomi, and CISO Global. Its SOC reports are issued by A-LIGN Assurance, a licensed CPA firm registered with the Public Company Accounting Oversight Board (PCAOB).
Its auditors tested how our security and confidentiality controls performed in real, day-to-day operation. That included who can access restaurant data, how sensitive information is kept confidential, and how our team is trained to handle it.
"When an operator chooses AIO, they're trusting us with their guest list, their payroll, and every sale that comes through the door. Completing SOC 2 Type II with A-LIGN shows that the way we protect that data holds up to independent scrutiny, month after month."
About SOC 2 Type II
SOC 2 is a globally recognized audit framework established by the American Institute of Certified Public Accountants (AICPA) for companies that store or process customer data. Auditors evaluate a company against the AICPA's Trust Services Criteria and formally review its infrastructure, software, people, data, policies, procedures, and operations. A Type I report assesses whether controls are designed correctly at a single point in time. A Type II report also tests their operating effectiveness, using evidence collected across a review period that typically runs 3 to 12 months.
Why it matters for restaurants
SOC 2 Type II is the standard larger buyers and franchise groups expect from their technology vendors, and it is held by leading restaurant technology providers. For restaurants on AIO, it means:
- Protected guest data: Guest names, contact details, and order history are safeguarded by independently tested controls.
- Confidential business information: Sales figures, menu pricing, and staff records are covered by confidentiality controls verified by an independent auditor.
- Faster vendor approvals: When your franchisor or IT team runs a vendor risk assessment, an independent report is ready to share.
"A Type II audit doesn't take your word for anything. A-LIGN pulled real evidence from our operations, from access reviews to code changes to how we responded to alerts, and checked it against the controls we committed to. That is the same discipline we bring to the platform every day."
Our commitment to security
Achieving SOC 2 Type II is part of a broader commitment. Through this process, we strengthened data security across the platform, increased protections for confidential information, and had those controls verified by an independent auditor. We will keep investing in and strengthening our security framework as AIO grows, so restaurants can run their business with confidence.